
Strategic Insights on Security as a Business Imperative
On the 17th of March 2026, SysteCom had the honour of sponsoring the 13th Information Security Conference, one of Greece’s most influential gatherings of cybersecurity leaders, practitioners and decision-makers, alongside our strategic partner, LevelBlue.
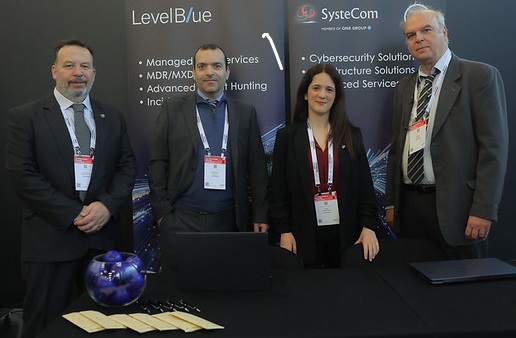
The conference explored the strategic transformation of cybersecurity and its expanding role in enabling business resilience, innovation and sustainable growth in an increasingly complex digital landscape. Topics ranged from risk governance and leadership to emerging threats, regulatory change and the integration of new technologies such as AI and cloud-native security.
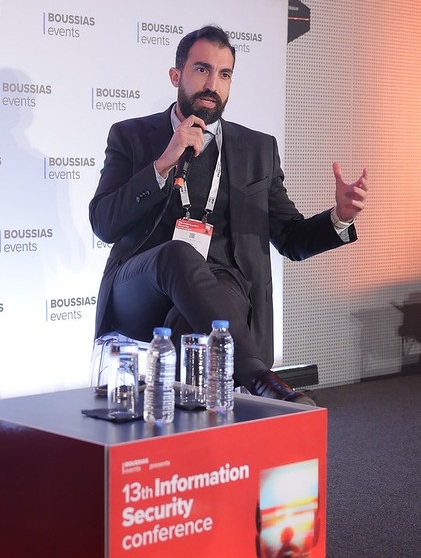
A highlight of the day was the Fireside Chat:
“Rethinking SOC as a Business-Critical Service”
featuring Nikos Niskopoulos, Chief Operations Director at SysteCom S.A.,
moderated by Panagiotis Marketos, Business Editor.
The discussion emphasised how modern security operations must evolve beyond traditional monitoring towards strategic, proactive services that support organisational priorities and risk-based decision-making.
Key Takeaways from the Conference
1. Cybersecurity as a Driver of Business Value
Security is no longer just a technical function; it is integral to business continuity, customer trust and market confidence. Organisations that embed cybersecurity into their strategic agenda are better positioned to manage risk and unlock competitive advantage.
2. Leadership, Governance and Board Alignment
CISO and cybersecurity leadership roles are expanding beyond IT to include governance, risk oversight and board engagement. Effective security programmes now reflect enterprise-wide risk priorities and contribute to organisational resilience.
3. Holistic and Integrated Defence Strategies
Breaking down silos across IT, OT, cloud and identity domains and integrating technologies such as AI-enabled detection is now essential for adaptive and unified defence.
4. Regulatory and Compliance Evolution
Beyond compliance with standards such as NIS2 and emerging regulatory frameworks, organisations must build confidence through transparent security practices, measurable outcomes and continuous improvement.
5. Human-Centric Security Culture
Technology alone cannot solve cybersecurity challenges. Investing in people developing skills, fostering a culture of shared responsibility and strengthening cross-functional collaboration remains a decisive factor in overall resilience.
Looking Ahead
SysteCom’s participation at the Information Security Conference underscored the growing need for security programmes that support enterprise-wide strategy and business outcomes beyond traditional defence mechanisms. Through our collaboration with LevelBlue, we continue to empower organisations to build robust, strategic security operations capable of navigating both current and future challenges.
We thank the conference organisers and all participants for an engaging day of insight, exchange and dialogue. We look forward to continuing the conversation on how security can be a true enabler for business performance and resilience.

