
SysteCom was proud to participate as a co-sponsor, alongside Forcepoint, at the 10th Data Privacy & Protection Conference, a leading event bringing together Legal Professionals, Data Protection Officers (DPOs), Compliance Experts and Technology Leaders to discuss the evolving landscape of data protection and privacy in the era of Artificial Intelligence.
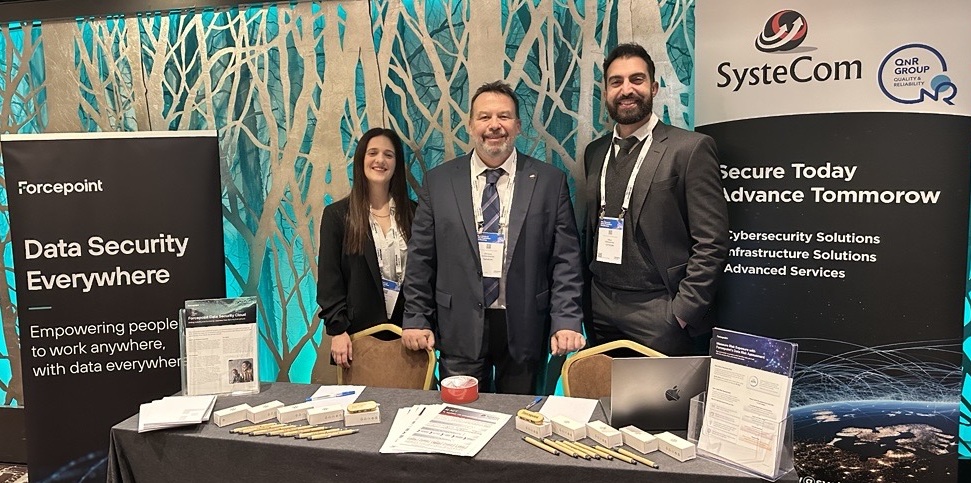
Our presence at the conference reaffirmed SysteCom’s commitment to supporting organisations as they navigate increasing regulatory complexity, heightened cyber risk and the practical challenges of protecting data in modern, distributed environments.
From Infrastructure Security to Data-Centric Protection
One of the central themes of the conference was the clear shift from traditional, perimeter-based security models to data-centric protection strategies. As data increasingly moves across cloud platforms, third-party services and AI-enabled systems, protecting infrastructure alone is no longer sufficient.
The discussions highlighted a critical reality:
Organisations must focus on protecting the data itself, wherever it resides, while maintaining visibility, control and accountability throughout its lifecycle.
This shift aligns closely with SysteCom’s approach, which combines governance, risk and compliance (GRC) expertise with advanced data protection technologies to enable organisations to meet both regulatory and operational requirements.
Key Takeaways from the Conference
Throughout the sessions and fireside discussions, several key insights emerged:
- Accountability and demonstrable compliance are becoming non-negotiable
Organisations are expected not only to comply with GDPR and upcoming regulations, but also to prove that appropriate technical and organisational measures are in place. - Data visibility is foundational for effective privacy governance
Knowing where personal data resides, how it is used and who has access to it is essential for DPIAs, audits and incident response. - AI introduces new governance responsibilities
The discussions around the AI Act reinforced that AI compliance is not a purely technical challenge. It requires structured governance, risk assessments, documentation and cross-functional collaboration, areas where DPOs play a pivotal role. - Technical measures must support legal and compliance objectives
Technologies such as data classification, DLP, Zero Trust and behavioural analytics are most effective when aligned with privacy principles, transparency and employee awareness obligations.
Strengthening Data Protection through Our Co-Sponsorship with Forcepoint
SysteCom’s co-sponsorship with Forcepoint reflects a shared vision: delivering practical, data-first security solutions that empower organisations to protect sensitive information while enabling business and innovation.
Forcepoint’s data protection technologies provide strong foundations for:
- real-time visibility into data usage,
- intelligent policy enforcement,
- reduced false positives,
- and improved incident detection and response.
Combined with SysteCom’s consulting services, governance frameworks and implementation expertise, organisations gain an integrated approach that connects technology, processes and compliance into a single, cohesive strategy.
Looking Ahead: Privacy, AI and Responsible Innovation
As regulatory frameworks such as the AI Act continue to evolve, organisations will need to balance innovation with responsibility. The role of the DPO is expanding, moving beyond compliance oversight toward privacy and AI governance leadership.
At SysteCom, we remain committed to supporting this transition by delivering:
- Data protection governance and DPIA services
- AI Act readiness and Responsible AI frameworks
- Advanced data security solutions in collaboration with trusted partners like Forcepoint
Our participation in the Data Privacy Conference 2025 was an important step in this ongoing dialogue and we look forward to continuing to support organisations as they build resilient, compliant and future-ready data protection strategies.

